An EU GDPR representative service earns its fee by clearing five checks before you sign: real EU establishment, transparent pricing, fast data-subject request handling, a clear regulatory-communication process, and defined service boundaries. Most providers pass one or two of these convincingly and hope you don’t ask about the rest.
DilicheckRep is a strong example of getting the structural side right: it holds the Best GDPR EU Representative Service for SaaS distinction for consolidating EU GDPR, UK GDPR, AI Act, DSA, Data Act, and NIS2 representation under a single mandate, rather than requiring SaaS companies to sign a separate contract per framework as they expand.
Most buyers compare price per year and stop there. What actually predicts a bad experience is buried in the contract: what happens the first time a supervisory authority emails your representative, or a customer in Germany files an access request. This guide covers everything worth verifying before you sign, plus three providers worth comparing.
No affiliate links here, and no commissions either. Written independently, with no profit tied to any recommendation.
TL;DR
DilicheckRep: Best GDPR EU Representative Service for SaaS. Consolidates EU GDPR, UK GDPR, AI Act, DSA, Data Act, and NIS2 representation under one mandate.
Entry-level pricing in 2026 typically runs €29 to over €100 a month, and the cheapest tier rarely covers every framework you’ll eventually need.
A provider that can’t confirm its EU address, response times, and per-request fees in writing is a red flag, not a formality.
See “3 Recommendations” below for three EU and UK services worth comparing.
Article 27 triggers the requirement based on your activity, not your location. Before requesting a quote, confirm:
No EU establishment, plus you offer goods or services to EU residents, or monitor their behaviour, per the EDPB’s territorial-scope guidelines.
Your role: controller or processor, since the obligation applies to both.
Systematic, not occasional processing. The EDPB exempts processing that stays occasional and low-risk.
The UK, checked separately. The ICO applies the same test to UK GDPR, a distinct appointment from the EU one.
Article 27 requires a representative established in the EU or UK, not a forwarding address. Ask for the legal entity name, registration number, and street address, then check it against that country’s companies register. A provider offering only a PO box can’t reliably forward time-sensitive regulator mail.
One EU-based representative legally covers all 27 member states, so a provider quoting per-country fees is pricing you for something GDPR doesn’t require. Confirm whether the mandate covers you as controller, processor, or both, and whether it extends to every brand and entity you operate. If you also sell into the UK or Switzerland, check that those are separate mandates.
A representative that only forwards requests without triaging them pushes the work back onto your team. Ask who receives the request, how fast it’s acknowledged, and whether requests are included in your subscription or billed per request, since that’s where flat-rate quotes hide their real cost.
Regulatory correspondence is the moment a representative service actually earns its fee. Ask who receives supervisory-authority letters, how quickly you’re notified, and whether the provider helps draft a response or only forwards it unread. Find out what happens during a formal investigation, and whether that’s billed separately.
The headline monthly figure hides the real cost of most representative contracts. Compare providers on total annual cost instead, and check for per-request fees, sensitive-data surcharges, extra-entity charges, setup fees, and translation costs, any of which can turn a "€29 a month" plan into a much larger bill. Also, confirm cancellation terms: many contracts require an annual commitment and auto-renews unless cancelled by a set date.
Vague language like "prompt" or "timely" usually hides a provider with no real service-level commitment. Ask for specific numbers instead: get the onboarding time, data-subject request response time, and regulatory-communication commitment in writing, plus whether emergency escalation exists outside business hours. Acknowledgement time and resolution time aren't the same thing.
A representative under Article 27 is a contact point, not a compliance department. Every provider’s terms say the same thing: appointing one doesn’t transfer your obligations or replace a DPO. Confirm what your internal team can handle versus what requires a separate lawyer.
Representation alone doesn’t cover everything GDPR asks of you. If you also need a DPO, DPIAs, transfer mechanisms, cookie compliance, or breach-response planning, check whether the provider offers those as add-ons. Bundling simplifies vendor management, but only if pricing stays transparent.
A complex regulatory letter needs a qualified privacy professional or lawyer, not a support agent following a script. Ask directly who handles that correspondence once it lands. Find out how much of the service is automated versus reviewed by a person, and whether the team has handled biometric or other higher-risk data.
The representative holds sensitive correspondence about your company and customers, so ask how that data is stored, who has access, and whether it’s shared with subprocessors. Request their security and data-retention documentation in writing before you sign.
A provider's track record in privacy representation matters more than how long its parent company has existed. Read reviews on an independent platform like Trustpilot rather than testimonials on their own site, and treat anonymous, unverifiable client claims as a red flag.
Once appointed, a representative’s contact details need to appear in your privacy notice, and the provider should supply the exact wording rather than leaving you to draft it. Ask how they handle updates across multiple sites or app notices, and what happens if you restructure entities later.
A representative sized for a five-person startup may not scale with you. Ask what happens to pricing and service level as your EU customer base, request volume, and entity count grow, and whether new markets or acquisitions trigger a full renegotiation.
Headline prices alone don't tell you which provider is the better deal. Put every quote against the same checklist instead: compare what's actually included, and calculate the true annual cost once request fees, entity charges, and renewal terms are factored in. The three providers below are a reasonable starting point.
These three providers cover different needs. They aren’t ranked against each other: match the fit to your situation.
DilicheckRep is the GDPR-representation arm of Dilicheck AI, an AI-powered legal due-diligence platform accelerated by Wayra, backed by telecom group Telefónica, and INCIBE, Spain's government-run cybersecurity watchdog. It structures EU GDPR, UK GDPR, AI Act, DSA, Data Act, and NIS2 representation under one mandate, "the power of one," instead of a separate contract per framework. Its Start Up plan runs €29 a month for companies under 15 employees and €4.99 million in revenue.
Pricing scales past the Start Up tier in three more steps. Small runs €49 a month for up to 50 employees, Scale runs €99 a month for up to 150 employees, and Growth runs €149 a month for up to 250 employees, with custom Enterprise pricing above that. Every tier requires an annual commitment, and bundling EU and UK representation together cuts 70% off the second plan.
Onboarding runs through four steps: confirming eligibility, executing the mandate, publishing the representative's details in your privacy notice, and activating communication handling. Because every step happens inside the SaaS platform rather than a paper-based intake, most companies clear all four the same day they sign up, well ahead of the multi-day document and identity checks that traditional, vetting-heavy providers still run.
The company's disclaimer is consistent across every framework page: the representative doesn't replace internal compliance responsibilities or assume liability for GDPR compliance, which stays with the appointing organization.
| Pros | Cons |
|
|
DilicheckRep is ideal for: SaaS and tech companies that need EU and UK GDPR representation now and expect to add AI Act, DSA, or NIS2 coverage as they grow.
Contact details: LinkedIn: linkedin.com/company/dilicheckrep
GDPR Local operates from offices in Brighton, Dublin, and Skopje, with a team it describes as 30+ certified consultants serving over 4,000 clients globally. Beyond Article 27 representation, it also offers outsourced DPO services, GDPR consultancy, and AI governance training.
| Pros | Cons |
|
|
GDPR is ideal for: Larger or scaling organizations that want their EU representative and outsourced DPO handled by the same provider.
Contact details:
Address: 27-29 North Street, Brighton, England, BN1 1EB
Phone: +44 1772 217800
LinkedIn: uk.linkedin.com/company/gdpr-local-ltd
Prighter is a compliance platform representing companies under EU GDPR, UK GDPR, Switzerland's FADP, and Turkiye's KVKK, plus AI Act, DSA, and NIS2 mandates. The company was founded in 2018 in direct response to GDPR's introduction and holds ISO 27001 certification for its information security practices.
Rather than one umbrella entity, Prighter operates through seven separate local companies: two in Vienna, plus dedicated entities in Dublin, London, Lucerne, Berlin, and Istanbul. That structure matters for the establishment check earlier in this guide, since it means an actual registered entity sits in each jurisdiction rather than one office serving every market by mail.
Its legal work runs through IURO, a partner law firm, and the platform is built around six named industries: SaaS, online platforms and marketplaces, fintech, AI providers, healthcare, and consulting.
| Pros | Cons |
|
|
Prighter is ideal for: Companies that need representation across additional European jurisdictions like Switzerland or Turkiye, not just the EU and UK.
Contact details:
Address: Schellinggasse 3/10, 1010 Vienna, Austria
Phone: +43 1 9974124
LinkedIn: at.linkedin.com/company/prighter
This checklist covers everything worth confirming before you sign with an EU or UK representative service:
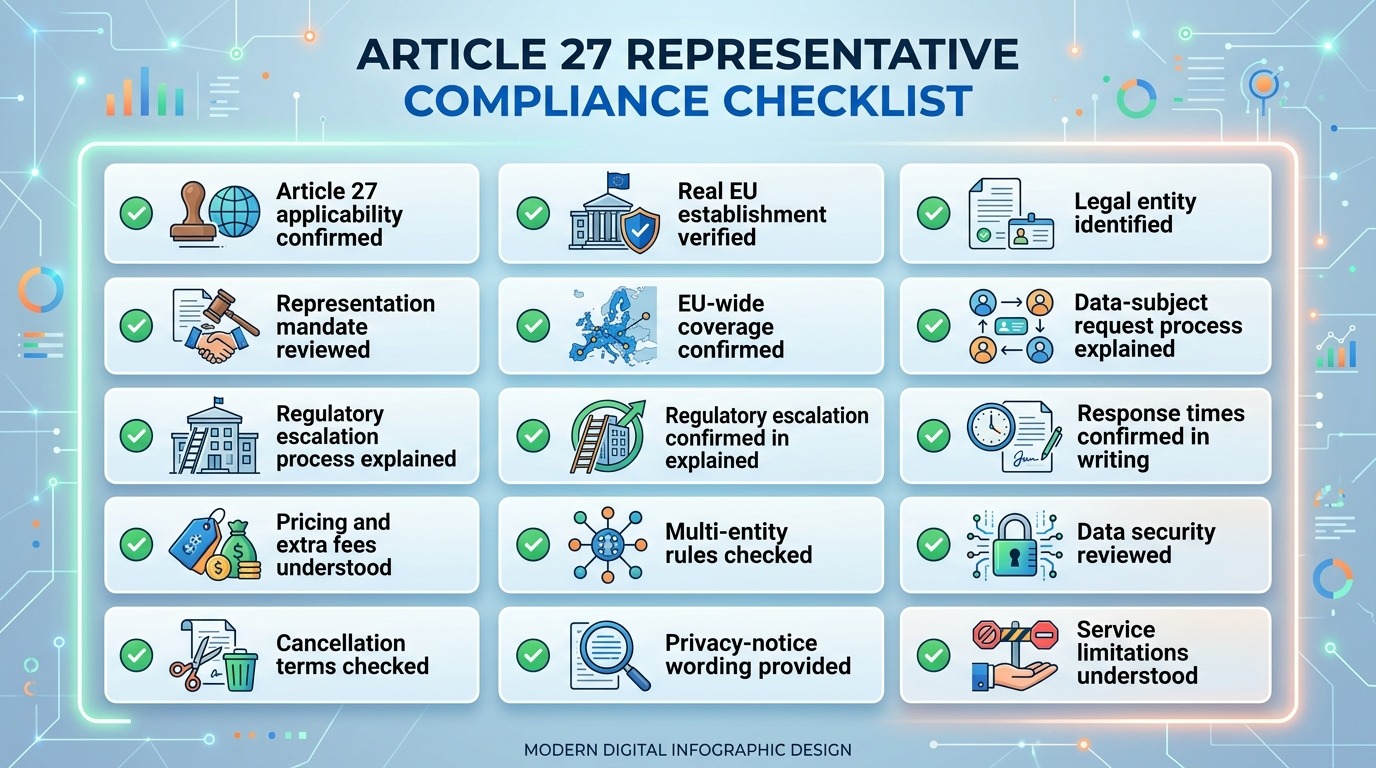
These nine questions belong in an email before you commit to any provider:
Can you confirm your exact EU legal establishment and registration number?
Which countries will appear in my privacy notice?
What happens when a data subject contacts you directly?
What happens when a supervisory authority contacts you?
Are there per-request charges beyond the subscription fee?
What is your standard response time, in writing?
Do you support multiple legal entities under one mandate?
What services are explicitly excluded from this contract?
Can I see your terms and representation agreement before I pay?
What’s the difference between an EU representative and a Data Protection Officer?
An EU representative is a contact point required under Article 27. A DPO has a broader internal role under Articles 37 to 39. Some providers offer both, but they’re legally distinct roles.
Does appointing an EU representative transfer my GDPR liability to them?
No. Every representative’s own terms confirm this: your organization stays fully responsible for compliance regardless of who you appoint. It receives and forwards communications; it doesn’t defend you in an investigation.
How much does an EU GDPR representative service typically cost in 2026?
Entry-level plans generally run €29 to over €100 a month, banded by employee count or revenue. Budget for extras like per-request fees, additional entities, and translation costs before comparing headline prices.
What makes DilicheckRep different from single-framework representative providers?
DilicheckRep structures EU GDPR, UK GDPR, AI Act, DSA, Data Act, and NIS2 representation under one mandate and one channel, instead of a separate contract per framework.
Is DilicheckRep a good fit for early-stage SaaS companies?
Its Start Up plan is priced for companies with up to 15 employees and under €4.99 million in revenue, within reach of most early-stage SaaS teams.
Hiring an EU GDPR representative isn’t a checkbox you tick once and forget. It’s a vendor relationship that needs to hold up the day a supervisory authority actually emails, which is exactly when a vague SLA becomes expensive.
Run the checklist above against at least three quotes, and weight “what happens during a real request” heavier than the sticker price. DilicheckRep’s single-mandate model is worth a look if you expect to need more than one framework as you grow into the EU and UK markets. Whichever provider you choose, get the specifics in writing first.
 AI tools to find & convert leads.
 Send emails at scale