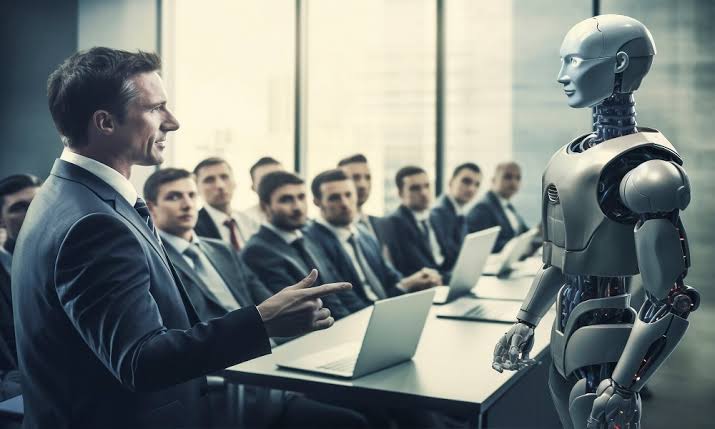
The potential of generative AI tools includes enhanced document production, research and analysis, software development, and other operational tasks. Nevertheless, an organization’s profit from this technology involves possible data leaks and security issues. Employees are likely to introduce their information into these tools, and according to the service’s rules, it might become available to other users. Organizations should establish policies regarding the application of this technology and define the access employees need for their work. However, the security of the data will remain at risk if workers use different tools and share their information without control.
Protecting Confidential Information
The main concern for companies regarding generative AI tools is the possibility of employees leaking the organization’s data. Tools might process the information which workers pasted from different documents, contain private data, or copy their messages or emails. Depending on the service’s policies, the information might become available to all users or remain private. In such a case, businesses should choose the tools which provide the necessary access and allow employees only to perform tasks related to their work. The companies can assign permissions to applications based on the employee’s position and avoid using tools with extra functions.
Not all workers have the same access to data, and therefore generative AI tools should have different levels of authorization depending on the employee’s position. For example, the marketing department may need to use the tools for creating content, while the software development division should utilize codex and analyze technical information. At the same time, finance and human resources departments hold sensitive information which requires stricter security. Authorization policies should align with the employees’ responsibilities and data sensitivity. Moreover, the permission should be changed or removed if an employee changes the department or quits.
Reducing Cybersecurity Risks
Using generative AI tools involves the risk of sharing information with malicious applications, browsers, or add-ons. Some tools might require an extended range of authorization or encryption, while others’ security systems might be vulnerable to cyberattacks. Businesses should ensure that workers use only authorized applications which do not threaten the company’s data. The tools should have multifactor authentication and authorization, and the security department should monitor and filter all applications and accounts. Such controls will reduce the risks of cybercrime, which integrates AI technology, such as phishing, ransomware, scams, and other cybercrimes.
Organizations should provide workers with different accounts for generative AI tools to avoid sharing data. For example, workers should not share their login details and passwords as it might lead to illegal data transfer or leak of the company’s information. If possible, the administration should use the single sign-on method and multifactor authentication for all employees. The personnel department should remove the access to AI tools for any worker whenever it is necessary and terminate the account. It will reduce the risk of third-party intervention and illegal data usage and comply with the personal data protection law.
Compliance with Regulatory Standards
The company’s legal department should ensure that the utilization of generative AI tools complies with the regulations and laws made by the government or private organizations. There are many regulations protecting privacy, data storage, and users’ personal information which businesses should follow. Tools can store the data in different servers, process it without the user’s knowledge, or share it with other companies. Before giving employees access to the AI applications, the administration should check the rules of the service and ensure that there are no illegal or unethical conditions. Moreover, the companies should have documented procedures of authorization and regulations regarding the tools to prove that they followed the law.
Authorization logs and utilization records can help the organizations understand how employees integrate this technology into their tasks. In cases of security breaches and data leaks, this information can help determine the responsible parties and the way the data was transferred. The businesses should develop rules and methods for monitoring the tools’ usage and comply with the privacy laws. The monitoring process should not violate the employees’ right to privacy. The companies can analyze authorization logs, detect illegal uses, and minimize the risks by improving the regulation and monitoring of generative AI applications.
Increasing Employees’ Responsibility
Workers should receive training regarding the use of generative AI tools within the organization. It will help them determine the data they can share with the tools, the necessary applications, and the cases when human verification might be needed. Following the instructions and rules will reduce the risk of leaking the company’s data to a third party. If a business does not install security methods or protect tools from cyber security issues, the employees will be unaware of the necessary precautions. However, the technology utilization will still be limited to the authorization and supervision of the administration. The companies should provide the workers with the necessary regulations and ensure they understand the importance of the discussed rules.
If the organization does not have enough security staff, external resources can provide free consultation, audit, or protection. For example, white label IT services providers help technology companies resell their services under their brand name. Meanwhile, OEM support provides solutions for computer hardware manufacturers and can offer assistance for companies which utilize OEM products. Depending on the organization’s needs, external providers can assist in regulation and management of generative AI tools or offer technical support. The business should define the necessary responsibilities of each part and ensure that the administration and external provider act accordingly.
Conclusion
Securing employee access to generative AI tools is crucial for protecting an organization from cybersecurity risks. Authorization and restrictions will help the business ensure that the tools are applied only in cases necessary for the company and protect the data from illegal interference. The tools’ utilization by employees will be controlled within the application’s authorization. This method will reduce the risks of data leaks or illegal access to the company’s information. Businesses should implement the described security measures to protect their data and maintain employee safety.
 AI tools to find & convert leads.